
October 14, 2026 —
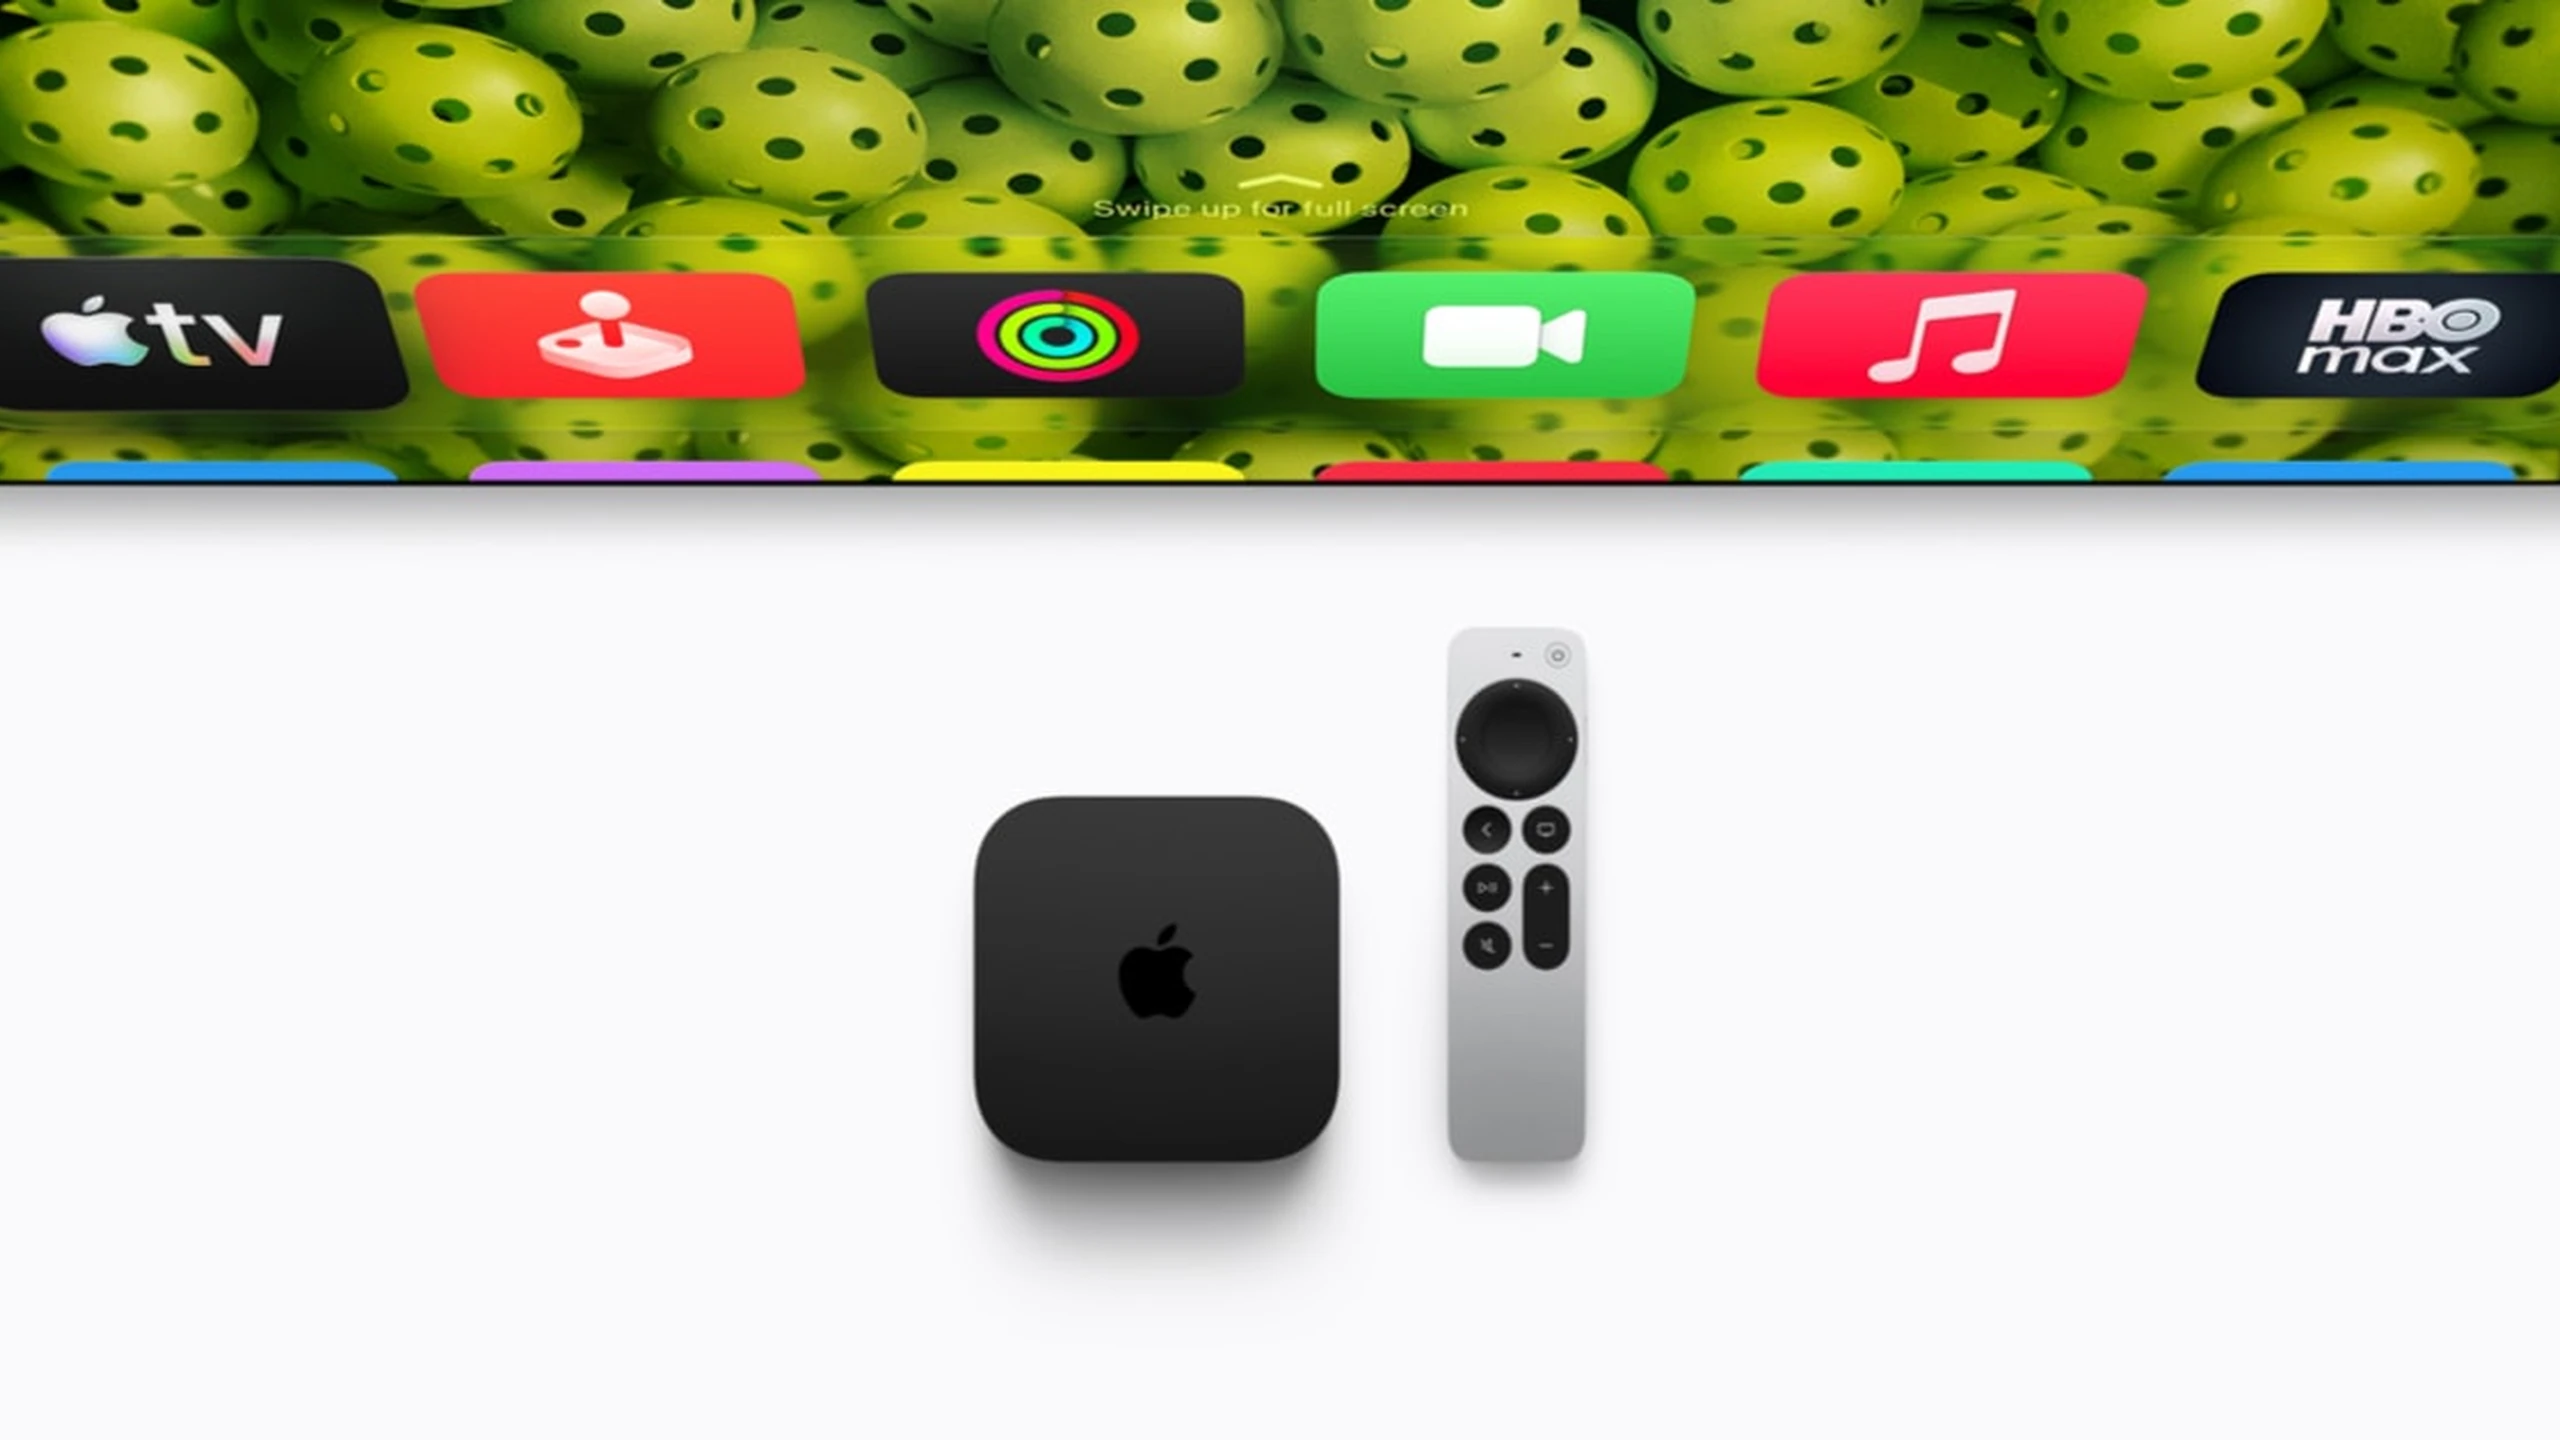
Apple TV adds room-scale Siri, but older boxes also get the assistant
Today's developments put AI closer to everyday actions: searching a television, selecting a product through glasses, compressing an agent's history or investigating a production trace. The useful distinctions are concrete. Which features need new hardware, what evidence survives compression, and what has actually been demonstrated? The security items also separate fixing an entry point from investigating access that may already have occurred.
Apple TV adds room-scale Siri, but older boxes also get the assistant
Apple announced its fourth-generation Apple TV 4K on October 13, with availability planned for November 13. An A19 chip, AV1 decoding and three far-field microphones support conversational entertainment search and hands-free home control. Apple claims up to 50% faster CPU performance and twice the GPU performance; those are company figures, not independent tests. The new hardware can coordinate four compatible HomePods, while earlier models remain limited to two in that configuration.
Siri AI itself will also reach second-generation Apple TV 4K and later in beta. Existing owners therefore do not need the newest box for every conversational feature. The launch beta supports English in eight markets, and a search based on a friend's recommendation requires an Apple Intelligence-enabled iPhone for personal context. Camera descriptions and HomeKit activity summaries extend the assistant beyond finding films, but their accuracy has not been independently established.
The upgrade case rests on direct room listening, audio coordination and hardware performance rather than the Siri label alone. Apple describes isolated microphone processing and protected cloud handling; those safeguards do not by themselves resolve whose private context should appear on a shared screen. Mixed-device homes and unsupported languages face a narrower experience than the launch demonstration suggests.
Alibaba's Qwen glasses make service access the wearable differentiator
Alibaba began selling Qwen Glasses N1 and N1 Pro in China on October 13 after September preorders. The N1 has a 50-megapixel sensor; the Pro adds eye tracking for object selection and payment-related interactions. The company describes shopping, translation, music and health features, with claimed battery figures of 25 hours standby or nine hours of music. Those figures do not measure mixed camera, network and assistant use.
The strategic difference from Meta is Alibaba's connected commerce, payments and local-service network. Recognizing an object can lead toward product lookup and a transaction rather than stop at an answer. That also increases the importance of explicit purchase approval, capture indicators and controls over voice, gaze and biometric information. Earlier international plans do not establish equivalent N1 service coverage outside China; comfort, prescription support and sustained use remain unproven by launch specifications.
ScaleDown separates agent context work from frontier-model reasoning
LangChain's new ScaleDown integration delegates summarization, compression, extraction and classification to specialized constrained-output models while the main model continues planning and generation. Tool compression uses a task-specific query to select relevant material; extraction reads user messages rather than treating the agent's own speculation as supplied facts. A LangSmith gateway path provides centralized credentials, policies and tracing.
The middleware fails open: a rejected or unavailable auxiliary call lets the agent continue without that transformation. Availability can therefore mask a larger context bill or missing extracted state. Summarization also has a private-preview boundary. Vendor speed and cost comparisons describe narrow operations, not the whole agent workflow. Compression can discard exceptions or instructions and change cache reuse, so the useful comparison is successful task completion, retained facts, retries and total latency with the original material recoverable.
LangSmith searches agent behavior, with an explicit evidence budget
LangSmith AI Search entered public beta on October 13. Reviewers can describe behavior such as a user becoming frustrated or an agent claiming success without completing a task, combine that request with conventional filters, and inspect confidence-ranked matches. The system normalizes repeated trace history into a trajectory and uses a decision model rather than relying solely on keyword or vector similarity.
Each trajectory has an 8,000-token budget that prioritizes user messages and final agent replies before intermediate operations. Decisive tool errors may fall outside that view; subagent, middleware and compaction content are not searched. Descriptions cannot yet be saved as views or preserved in shared links. Administrator enablement permits processing in the United States even for other hosting regions, and the feature excludes protected health information and BAA coverage. Confidence is not proof: inspect the recorded evidence and turn recurring findings into tested evaluators.
Anthropic demonstrates replication components, not an autonomous IoT worm
Anthropic's controlled research separates model deployment on unfamiliar hardware from end-to-end propagation. Qwen3.5-9B configured inference on eight of nine hardware types. A separate distributed model ran across 15 Android TV boxes at 0.39 tokens per second, showing feasibility but not practical interactive speed.
In a firewalled eight-node emulator network with deliberately unauthenticated maintenance access, GLM-5.2 reached all nodes in four of five trials and seven in the other. The capable orchestrator ran on an external server, not on those weak targets. Smaller models that fit the devices did not reliably complete the entire sequence. Inherited troubleshooting notes improved later setup attempts without retraining model weights. The outstanding risk is convergence between small-model capability and deployability, not evidence that such malware has escaped into households.
Ivanti's exploited gateway flaw needs investigation as well as a patch
CISA added Ivanti Connect Secure CVE-2026-104935 to KEV on October 13 after observed exploitation. The flaw permits unauthenticated command execution on affected branches. Volexity traced activity to October 3 on a release that was current at the time; its investigation found credential theft, directory queries and preparation for further access. The campaign's full scale and ultimate objective remain unknown.
The operator repeatedly used the exploit channel rather than leaving a conventional persistent web shell, restored temporary changes and removed selected logs. A clean disk-integrity result therefore cannot establish that prior access never happened. Fixed releases close the documented entry and execution path, while a separate privilege-escalation fix was still pending in the source report. Branch-specific updating, evidence preservation and review of gateway-accessible secrets address different parts of the incident; none should be recorded as a substitute for the others.
CISA's October 16 deadline covers two different response tracks
The October 13 KEV additions paired the Ivanti flaw above with Windows Shell CVE-2026-96951 and set an October 16 remediation deadline for federal civilian agencies. The Windows record describes a high-severity command-injection/security-bypass issue requiring user interaction; the Ivanti path requires no such interaction. Windows fleet deployment and gateway incident response are therefore distinct workloads even though both have confirmed exploitation evidence.
KEV inclusion does not establish that every affected machine is compromised, identify a universal delivery mechanism or prove ransomware use; the catalog's ransomware field is unknown. Private organizations do not inherit the federal deadline's legal obligation. The operational lesson is to verify affected builds, exposure and completed remediation rather than count update tickets, while preserving enough telemetry to investigate activity before the fix.